


 Network Security
 Vulnerability Management
 Privileged Access Management
 Endpoint Security
 Threat Hunting
 Unified Endpoint Management
 Email & Collaboration Security


Contents:
A normal week can look like this. Your insurer’s renewal form asks whether you run EDR (software that watches laptops and servers for attacks), keep offline backups, and use MFA (a second login step) on every admin account. A supplier emails new bank details just as a large invoice falls due. A scan turns up a firewall nobody has patched since spring.
None of these is a crisis yet, and each one asks the same thing. What should cybersecurity for SMBs include, and who should run it?
This guide is for small and medium-sized businesses (SMBs). It covers the risks, the first steps to take, and seven platforms worth a trial. We make the first one, Heimdal® XDR, and we say so wherever it appears.
The bottom line
Short on time? This is who each platform suits best.
- Heimdal® XDR. For small teams that want patching, DNS filtering, admin-rights control, and endpoint protection in one program on each device, bought as individual modules or as a managed service.
- Sophos. For businesses that want endpoint protection, a firewall, and 24/7 managed monitoring from one vendor.
- SentinelOne. For growing businesses with some in-house IT that want endpoint protection that can respond to attacks automatically.
- Trend Micro (TrendAI). Device and email protection in one Worry-Free bundle, for Microsoft 365 businesses.
- Trellix. For mid-market firms already buying through AWS. Its main focus is larger organisations, so very small businesses should check that its offering fits their size and staffing.
- Bitdefender GravityZone. For businesses with a small number of devices that want strong independent lab results.
- Cynet. Broad coverage in one program, with managed 24/7 response available, for businesses with one or two IT staff.
Why attackers keep reaching small businesses
You’re not too small to be a target. In Verizon’s 2026 Data Breach Investigations Report (DBIR), organisations with 1 to 1,000 employees accounted for 7,153 breaches where the victim’s size was known, against 466 for organisations with more than 1,000. Verizon doesn’t record size for every breach, so treat that as a strong signal rather than an exact ratio.
Many cyberattacks on smaller businesses aren’t personal. Verizon describes many of them as opportunistic, aimed at whoever has stolen logins or unpatched internet-facing devices. The most common known way into SMB breaches was exploiting software flaws that hadn’t been fixed (26%), ahead of stolen logins (13%) and phishing (9%).
Suppliers matter too. Verizon found a third party involved in 55% of SMB breaches, which includes flaws in a supplier’s software and breaches at suppliers that hold your data. Your IT provider, your accounting software, and your payroll platform all count.
The UK government’s Cyber Security Breaches Survey 2025/26 counts any attack a business noticed, including phishing emails that went nowhere. In it, 42% of micro businesses (1 to 9 staff), 46% of small businesses (10 to 49) and 65% of medium businesses (50 to 249) reported a breach or attack in the previous 12 months. Phishing was the most common type, reported by 88% of the businesses that identified one. Our small business cybersecurity statistics page collects more of the numbers.
What an attack costs a smaller business
Ransomware (malware that locks your files and demands payment) was present in 48% of breaches in the 2026 DBIR. The median ransom paid was $139,875, and 69% of victims did not pay. According to Verizon, about 96% of ransomware victims of known size were small organisations.
Smaller organisations are less likely to stop a cyberattack in time. In Sophos’s State of Ransomware 2026 survey of organisations hit by ransomware, only 34% of those with 100 to 250 employees stopped the ransomware attack before encryption or extortion, against 46% of those with 3,001 to 5,000.
Email fraud, such as a fake invoice or changed bank details, costs money without any malware at all. The FBI’s 2025 IC3 Annual Report logged 24,768 business email compromise complaints and about $3.05 billion in reported losses, second only to investment fraud.
Most incidents cost little in direct money. In the UK survey, the median perceived cost of a business’s most disruptive breach or attack was £0, or £200 when businesses reporting no cost are left out. The rare severe cases are what hurt. Verizon’s 2026 Breach Impact Study reviewed about 70,000 US cyber-insurance claims. For businesses with under $25 million in revenue, the most extreme 2.5% of claims came to more than 7% of revenue.
A breach that exposes customer information or employee data can trigger data protection obligations, regulator notifications, and claims. Customers send security questionnaires, and in practice many cyber insurers ask about MFA, EDR, and backups before they quote. Regulated businesses may also need to show evidence of controls for rules and schemes such as HIPAA, PCI DSS, NIS2, and Cyber Essentials.
Cybersecurity tips for small businesses
CISA’s Cyber Essentials guide in the US, the NIST CSF 2.0 Small Business Quick-Start Guide, and the NCSC’s guidance for small organisations agree on a short baseline of cybersecurity best practices covering MFA, updates, backups, malware protection, and staff awareness. The UK’s Cyber Essentials v3.3 requirements, which apply to new assessments from 27 April 2026, cover five areas (firewalls, secure setup, security updates, who gets access to what, and malware protection), require MFA on cloud services wherever it is available, and give more prominence to backups.
- Turn on MFA everywhere it matters. Email, cloud apps, remote access, and admin accounts first. Only 47% of UK businesses had any two-factor authentication in place in the Cyber Security Breaches Survey 2025/26.
- Update internet-facing devices first. Apply security patches to firewalls, VPNs, and anything else reachable from the internet, then to everything else.
- Keep backups offline or immutable. That way ransomware can’t change them. Test a restore every quarter.
- Make sure someone answers alerts. EDR without a responder is a log file. If that someone isn’t you, an MSP or MDR service can do it.
- Separate admin accounts. Nobody should browse the web or read email with admin rights.
- Train staff on fraud, not only phishing. Cybersecurity training should include SMS, voice calls, and fake invoices. Only 14% of UK micro businesses and 33% of small businesses reported providing staff training in the 2025/26 survey.
- Review supplier access. Know which third parties have access to your systems and remove what they no longer need.
- Write an incident response plan. List your insurer, IT provider, and law enforcement contacts before you need them.
- Set an AI-use policy. Say which AI tools staff may use and what sensitive data they must not paste in. Verizon’s 2026 DBIR found that 45% of employees in its data were regular AI users on corporate devices, and 67% of users reached AI services through non-corporate accounts.
You don’t have to do all nine at once. MFA, updates, and tested backups address the most common ways in and give you the best route to recovery.
Essential security tools for small and medium businesses
Most of these tools appear in CISA, NCSC, or NIST guidance for smaller organisations, and the rest are common additions. You don’t need all of them on day one, and the right mix depends on your size and security risks.
- Firewalls. A firewall filters traffic between your network and the internet. Firewalls and VPN gateways face the internet, so keep them updated.
- Next-generation antivirus (NGAV). Modern antivirus software that watches how files and programs behave, so it can flag malicious activity it has never seen before. Older signature-based antivirus software mainly catches threats it already knows.
- Endpoint detection and response (EDR). EDR records activity on laptops and servers, raises alerts on suspicious behaviour, and lets someone isolate an infected device or stop a process. It only helps if someone, in-house or at a provider, responds to those alerts. Our guide to XDR explains how EDR extends across email, network, and identity.
- Multi-factor authentication (MFA). MFA adds a second proof of identity, such as a code or a key, on top of your password. Prefer phishing-resistant methods such as passkeys or hardware security keys (FIDO2). In Sophos’s 2026 survey of organisations hit by ransomware, 97% of those whose attack began with compromised credentials had MFA in some form. Sophos says MFA alone isn’t enough and that gaps in coverage are where attackers get in, so switch it on for every login, including VPNs and firewall admin consoles.
- Password management. A password manager lets staff use long, unique passwords without remembering them, and makes it easier to remove access when someone leaves.
- DNS filtering. DNS security blocks connections to malicious websites and can stop malware already on a device from calling home.
- Anti-ransomware. Ransomware Encryption Protection watches for unauthorised mass file encryption and blocks it.
- Patching. Automated patch management installs operating system and third-party updates without someone doing it by hand. Verizon’s 2026 DBIR found organisations fully fixed only 26% of critical, actively exploited vulnerabilities on CISA’s list of known exploited vulnerabilities, and the median time to fully fix them rose from 32 to 43 days.
- Privileged access management (PAM). PAM is a type of access control that limits and records the use of admin accounts. A common approach removes permanent admin rights and grants elevation only when a task needs it, with a record of who did what. It puts the principle of least privilege into practice.
- Email security. Filters phishing, malicious links and attachments, and impersonation attempts. Train for other channels too. In the 2026 DBIR’s phishing simulations, SMS and voice lures had a median click rate about 40% higher than email, roughly 2% against 1.4%. Verizon notes that its sample of SMS and voice tests was small.
- Remote access. Remote desktop and VPN access should require MFA, be limited to named users, and be logged.
- Backup. In Sophos’s 2026 survey, 66% of victims whose data was encrypted recovered it from backups.
The four ways SMBs buy protection
Small business cyber security solutions now come in four main buying models. Budget, in-house skills, and compliance needs decide which one fits, and many businesses combine two.
A unified security platform
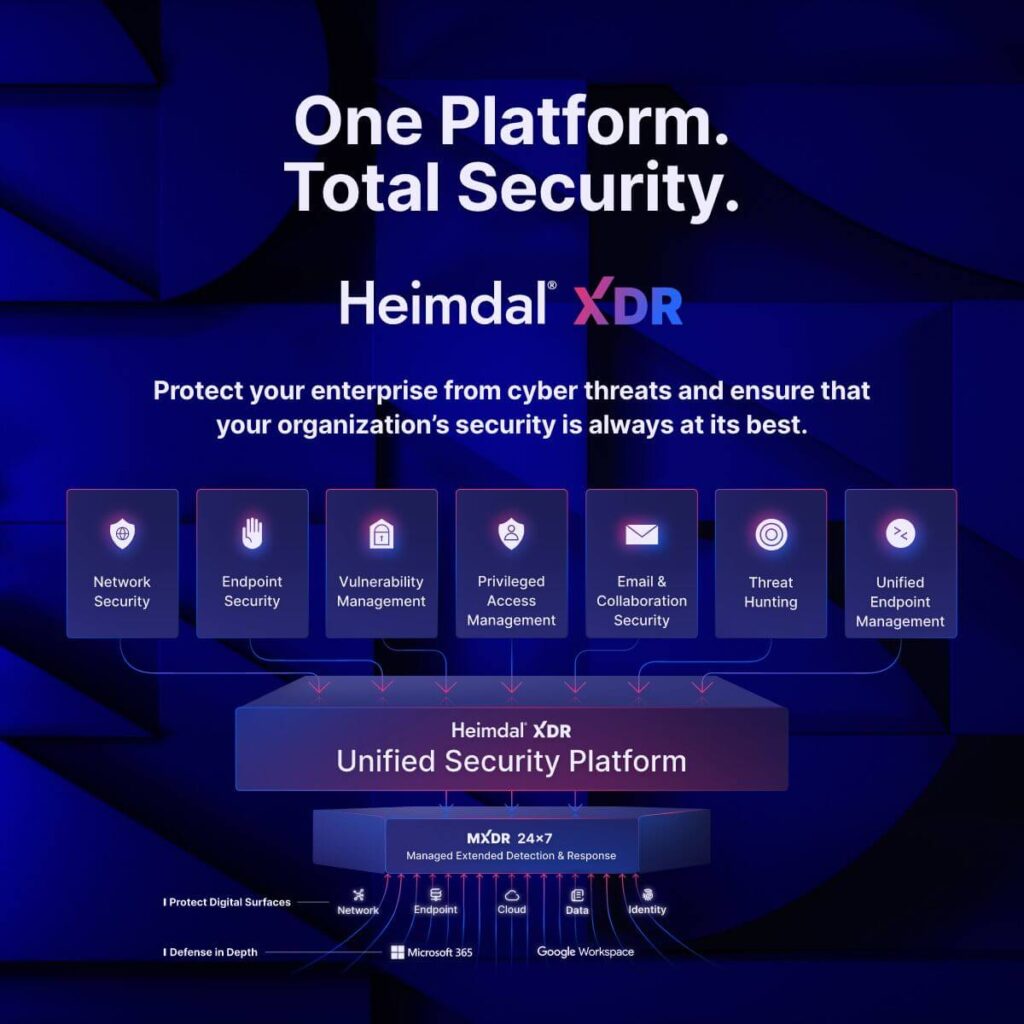
A unified platform runs several security tools from one agent (the small program installed on each device) and one console (the place where you manage them). You get one place to check alerts, one update cycle, and one view of each device. For a two-person IT team, that can mean reviewing alerts every day instead of only when something breaks.
Where Heimdal fits
We built Heimdal around this model, with one difference. Most of our modules can be bought on their own, including DNS security, endpoint protection, patching, privileged access, and email security. A few add-ons and managed services build on a base module, so confirm the combination with sales. You can buy Heimdal in three ways:
- As a standalone point product. Buy only the module that closes your gap, and sales will confirm if it needs a base module.
- As the unified platform. Run several or all modules from one console, with the endpoint modules sharing one agent on each device.
- As a managed service. Our SOC runs MDR, MXDR, or Managed ITDR for you around the clock, so you don’t need to staff it in-house.
Take a 60-person firm that already has a device management tool it intends to keep. Its real gap is third-party patching, patch reporting, and knowing what software sits on which laptop. It can buy Heimdal Patch and Asset Management on its own and run it alongside the existing tool. If it later wants DNS filtering, it can add it in the same console, and MDR can follow once the endpoint modules are in place.
A managed security service provider (MSSP) or MDR service
An MSSP monitors your security tools and alerts, often 24/7, and escalates what it finds. An MDR provider goes further and investigates and responds to threats on your behalf. Managed cybersecurity services for small business work best when the contract states what the provider can do without asking you first, such as isolating a laptop at 2am. The UK survey found 64% of small and 70% of medium businesses already have an external cyber security provider of some kind. Read more about managed security services.
A managed service provider (MSP)
An MSP runs your wider IT, from laptops and Microsoft 365 to backups and networking, and usually includes some security. For businesses with no IT staff, the MSP often chooses the security tools. Ask which products it uses, who responds to security alerts out of hours, and whether that response is in the contract.
Single-purpose tools
Separate tools from different vendors can work, and some businesses keep a specialist tool they rely on. The cost shows up over time.
Agent Fatigue. Each tool usually brings its own agent, and each agent is privileged software running on every device, which gives attackers more to target. Each one also adds a console to check, an update cycle to track, and an alert stream to triage. That load can quickly outgrow a small team, and an alert that sits in a console nobody opened that week is how a contained incident becomes a breach.
What to check before you shortlist
Signs your current setup isn’t enough
- You run antivirus but no EDR, and nobody reviews alerts outside office hours.
- Nobody at the business is clearly responsible for security.
- Critical patches wait weeks because someone has to install them by hand.
- Your insurer or a large customer has asked for security controls you can’t evidence.
- Your IT person checks four or more security consoles.
- Admin rights are permanent on staff laptops.
What to evaluate
- Coverage of real entry points. Edge and third-party patching, identity and MFA, email and endpoint.
- Who responds out of hours. The provider’s response authority and service-level agreement (SLA), in writing.
- Total cost. Licences, add-ons, MDR and the staff time each tool consumes.
- Manageability. How many agents and consoles you end up with, and who has time to run them.
- Evidence. Independent tests from the last 12 months, analyst coverage, and peer reviews. MITRE ATT&CK Evaluations Enterprise 2025 had only 11 participants, so lab tests from AV-Comparatives and AV-TEST fill gaps.
- Compliance fit. Cyber Essentials v3.3, NIST CSF 2.0 and your insurer’s questionnaire.
- Backup and recovery. How fast you can restore, and whether you have tested it.
What a tool won’t fix
No platform approves invoices for you. Payment changes still need a phone call to a known number. A tool won’t test your backups, write your incident response plan, or decide who your insurer, IT provider, and police contacts are.
How to run a trial
- Install on a small group of devices, 10 to 20 if you have that many, including at least one remote laptop and a server if you have one.
- Time how long a new critical patch takes to reach every trial device.
- Trigger a test alert at night and check who sees it and what they do.
- Compare published evidence, such as lab results or MITRE ATT&CK coverage mappings, for each vendor.
- Price three years, including add-ons and MDR, before you compare quotes.
Seven platforms worth shortlisting
Vendors reprice and repackage cyber security solutions for small business often, so we don’t quote competitor prices here. Confirm current pricing with each vendor or its partner. All other details are as of October 2026.
| # | Vendor | Best fit | Main coverage |
|---|---|---|---|
| 1 | Heimdal® XDR | Tool consolidation on one agent, with modules added as needed | Endpoint, DNS, patching, privileged access, email, and MDR |
| 2 | Sophos | Endpoint, firewall and MDR from one vendor | Endpoint, firewall, and MDR |
| 3 | SentinelOne | Automatic response for SMBs with some IT capacity | Endpoint, with XDR options |
| 4 | Trend Micro (TrendAI) | Endpoint plus email for Microsoft 365 businesses | Endpoint and email, with XDR options |
| 5 | Trellix | Mid-market XDR | XDR, endpoint, email, and network |
| 6 | Bitdefender GravityZone | Small fleets that want strong lab results | Business endpoint security, with XDR and MDR options |
| 7 | Cynet | Broad coverage with managed response | Endpoint, XDR, and managed response |
1. Heimdal® XDR
We publish this guide, so read our entry with that in mind.
What it is. Our modular security platform, sold as individual modules, as one unified platform, or as a managed service.
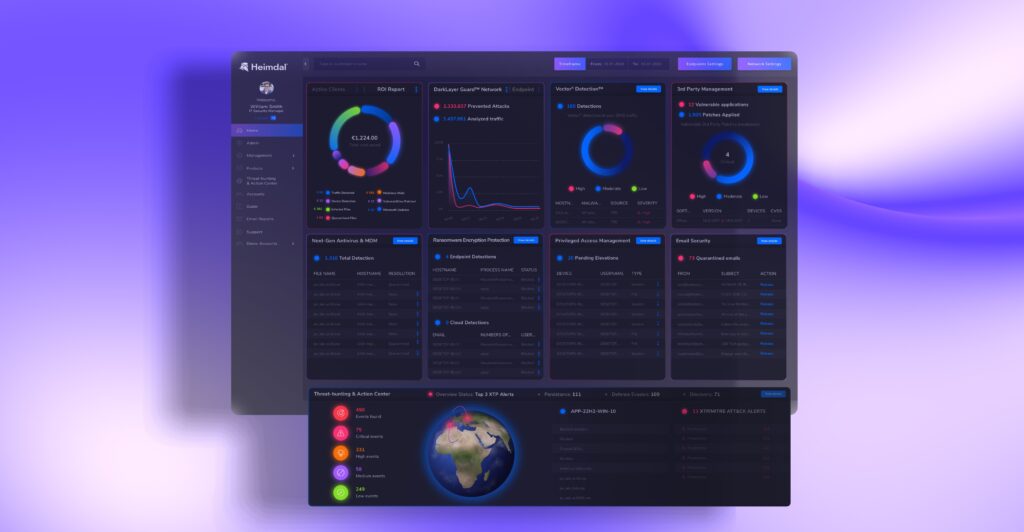
One agent. One console. One contract.
- DNS Security, which blocks malicious sites on the network and on endpoints, including Predictive DNS
- Next-gen antivirus, firewall, and Ransomware Encryption Protection
- Patch and Asset Management for Windows, macOS, Linux, and 350+ third-party applications
- Admin-rights control through Privilege Elevation and Delegation Management (PEDM) and Privileged Account and Session Management (PASM), plus Application Control with AppFencing™
- Email Security, with AI-powered Email Fraud Prevention on the Advanced Threat Protection option
- Remote Desktop
- Threat-hunting and Action Center (TAC)
- Managed detection and response (MDR, MXDR, and Managed ITDR) from our 24/7 security operations centre (SOC)
You switch on the modules you need now and add others later from the same console.
Best for. SMBs with a small IT team that want fewer agents and consoles, and businesses that want one specific gap closed without replacing tools that already work.
Strengths. Patching, DNS filtering, and privileged access run in the same agent as endpoint protection. Our patching can deliver updates within four hours of the vendor’s release, including testing, depending on your deployment schedule. Two AI-powered protection features are already live. Predictive DNS uses AI and machine learning to identify malicious domains before threats materialise. Our email fraud prevention uses outlier detection to catch impersonation, CEO fraud, and out-of-character messages.
AI Wingman is an assistant layer we’re rolling out across the platform in phases through 2026. AI Wingman Assist guides admins to the right settings in the dashboard. AI Wingman Triage comes with TAC and helps validate incidents. AI Wingman SOC comes with TAC and MXDR and helps our managed SOC analysts investigate faster. Ask us which parts are live for your plan.
Evidence. We serve over 20,000 companies. We are referenced in Gartner’s Endpoint Protection coverage (May 2026), and we are named as a representative vendor in Gartner’s Market Overview for Workspace Cybersecurity Platforms. We are also in an active analyst relationship with Forrester. In January 2026 we announced OPSWAT Gold Certification for Anti-Malware for our Next-Gen Antivirus with XTP.
We did not take part in MITRE ATT&CK Evaluations Enterprise 2025. Our MITRE ATT&CK technique coverage for Heimdal XDR is published on the Tidal Cyber Registry, where a free Community Edition account lets you review it and add it to your proof-of-concept scorecard alongside the other vendors on your list.
Trade-offs. Public independent lab testing of the full business XDR stack is limited, so test it on your own devices and judge detection there. If you buy several modules at once, expect more policies to set up in the first weeks.
Pricing. Our pricing calculator gives an instant estimate on the page and by email once you choose modules, enter your endpoint and server numbers, and add your business contact details. Final pricing is confirmed with sales. Public-sector and NGO rates are available, and businesses can start with a 30-day free trial. See the XDR platform page for module details.
2. Sophos
What it is. Sophos sells endpoint protection, 24/7 managed detection and response (MDR), and a firewall, managed from one cloud console. Product and console names are changing during 2026, so confirm exactly what a quote covers.
Best for. SMBs that want endpoint protection, a firewall, and managed monitoring from one vendor.
Trade-offs. Ask how third-party application patching would be covered in the tier you’re quoted. Sophos UTM/SG, an older firewall product, reached end of life on 30 June 2026. If you still run it, move to Sophos Firewall or another firewall.
Pricing. Check current pricing and packaging with Sophos or a Sophos partner. Our Sophos alternatives guide compares other options.
3. SentinelOne
What it is. The Singularity platform is AI-driven endpoint protection that can respond to threats automatically, with options that extend to XDR.
Best for. Growing SMBs with some in-house IT capacity, or businesses buying through an MSP, that want automatic response.
Trade-offs. Teams without staff to respond to alerts may need managed response, so check what’s included in your quote.
Pricing. Check current pricing and packaging with SentinelOne or a partner. For a head-to-head, see CrowdStrike vs SentinelOne.
4. Trend Micro (TrendAI)
What it is. Trend Micro’s SMB line is Worry-Free Services, with Worry-Free Services Advanced adding email and collaboration protection. XDR and Managed XDR options sit above it. Trend Micro renamed its enterprise business TrendAI on 23 March 2026, and its platform is now TrendAI Vision One, so you may see both names on a quote. Trend Micro remains the parent company.
Best for. Microsoft 365 businesses that want endpoint and email protection in one bundle.
Trade-offs. Confirm which product and console a quote covers, because two brand names are in use. Ask how third-party application patching would be handled.
Pricing. Check current pricing and packaging with Trend Micro or a partner.
5. Trellix
What it is. Trellix focuses on XDR, endpoint, email, and network security for larger organisations and mid-market buyers, and it lists XDR platform components on AWS Marketplace.
Best for. Mid-market firms, especially those already buying through AWS.
Trade-offs. Trellix’s main focus is larger organisations, so check that its offering fits your size and staffing.
Pricing. Check current pricing and packaging with Trellix, its AWS Marketplace listing, or a partner.
A note on McAfee. Trellix and McAfee are separate companies. Trellix was formed from McAfee Enterprise and FireEye, and McAfee kept the consumer brand. McAfee’s small-business product, McAfee Business Protection, is sold through Dell, so check its current terms with Dell if it’s relevant to you.
6. Bitdefender GravityZone
What it is. GravityZone is Bitdefender’s business security range, from small-business packages up to EDR, XDR, and MDR options.
Best for. SMBs with a small number of devices that want strong independent test results.
Strengths. In AV-Comparatives’ Business Security Test (March to June 2026, published July 2026), GravityZone Business Security Premium scored 99.8% in the real-world protection test and 99.5% in the malware protection test.
Trade-offs. Check which of patch management, email security, and full-disk encryption are included in the tier you’re quoted.
Pricing. Check current pricing and packaging with Bitdefender or a partner.
7. Cynet
What it is. An all-in-one platform that Cynet describes as one agent and one console, with 24/7 managed detection and response from its CyOps team.
Best for. SMBs with one or two IT staff that want broad coverage and managed response.
Trade-offs. Confirm which packages include CyOps 24/7 MDR before you compare.
Pricing. Check current pricing and packaging with Cynet or a partner.
For a wider comparison of detection platforms, read our guide to choosing the best XDR.
What cybersecurity for SMBs costs in 2026
Licence price is only part of the bill. A realistic budget covers four things:
- Licences per device or user
- Add-ons such as patching, email security or encryption
- MDR or MSP fees if someone else responds to alerts
- Staff time spent running each tool
Our pricing calculator returns an instant estimate for the modules you choose once you add your device numbers and business contact details. For other vendors, ask for current pricing in writing and compare like for like. If you already pay for Microsoft 365 Business Premium, Microsoft Defender for Business is included, so price the gaps around it rather than starting from zero.
Compare the total against the rare worst case, not the typical incident. A three-year view also shows the cost of tool sprawl, because every extra console adds hours that never appear on an invoice. Our page on security for SMBs sets out how our modules map to smaller teams.
Choosing by situation
Good cybersecurity for SMBs starts with the entry points attackers use most in Verizon’s data, which are unpatched systems, stolen credentials, and email, along with the suppliers whose software and access sit behind many of them. Match the buying model to who will respond when something happens.
- If you have no IT staff. Use an MSP or MDR service and check that out-of-hours response is in the contract. A managed service from Heimdal or Sophos, or Cynet’s CyOps service (confirm which packages include it), fits here.
- If you have one to five IT staff and too many consoles. A unified platform cuts the number of agents and alert streams. Heimdal runs its endpoint tools on one agent.
- If you have one clear gap, such as patching or admin rights. Buy the standalone module and keep what works. Heimdal sells most of its modules on their own.
- If you want endpoint protection, a firewall, and 24/7 monitoring from one partner. Sophos, moving off UTM to Sophos Firewall if you haven’t already.
- If you have some in-house IT skills. SentinelOne for automatic response, or Bitdefender for a small number of devices and strong lab results.
- If Microsoft 365 email is your main worry. Trend Micro Worry-Free Services Advanced, or compare it with Defender for Business if you already pay for Business Premium.
- If you’re closer to mid-market, with a security team and AWS procurement. Trellix.
FAQ
Where should a small business start with cybersecurity?
Turn on MFA for email, cloud apps, remote access, and admin accounts. Keep devices and firewalls up to date, and keep backups you’ve tested restoring. Then decide who will respond to alerts, whether that’s you, an MSP, or an MDR service. The tips above cover the full list.
Are small businesses really targeted by cybercriminals?
Yes, often through opportunistic attacks that don’t check company size. Where victim size was known in Verizon’s 2026 DBIR, 7,153 breaches involved organisations with 1 to 1,000 employees and 466 involved larger ones.
Is antivirus enough for a small business?
Usually not. In Verizon’s 2026 DBIR, the most common known ways into SMB breaches were exploited software vulnerabilities (26%) and credential abuse (13%), ahead of phishing (9%). A third party was involved in 55%, a figure that includes flaws in suppliers’ software. In practice, antivirus alone does little against the first two. Pair endpoint protection with patching, MFA, backups, and someone who responds to alerts.
What is the difference between an MSP and an MDR service?
An MSP runs your general IT and may include some security tools. An MDR service watches security alerts 24/7 and responds to threats. Many SMBs use both, so check which one is responsible for out-of-hours security response.
Is Microsoft Defender enough for a small business?
Microsoft Defender for Business is included in Microsoft 365 Business Premium, so it’s a sensible first thing to switch on if you already pay for that plan. Then ask it the same questions you’d ask any tool. Who responds to alerts outside office hours? How are non-Microsoft apps patched? Can you evidence your controls to an insurer or a customer?
How much should a small business spend on security tools?
It depends on device count and whether you need managed response. Ask each vendor for current pricing in writing, and include add-ons, MDR, and staff time on top of the base licence.
How does Heimdal pricing work?
Our pricing calculator gives an instant estimate on the page and by email once you choose modules, enter your endpoint and server numbers, and add your business contact details. Final pricing is confirmed with sales, and businesses can also start with a 30-day free trial.

- End-to-end consolidated cybersecurity;
- Complete visibility across your entire IT infrastructure;
- Faster and more accurate threat detection and response;
- Efficient one-click automated and assisted actioning
Conclusion
The number of cyberattacks on SMBs is rising. Hackers don’t just target large enterprises; small businesses are equally vulnerable to phishing attacks, social engineering, and ransomware.
Preventing an attack is far cheaper than paying for the consequences. Unified cybersecurity platforms, such as Heimdal’s XDR, offer comprehensive protection and simplified management, making them the best choice for small businesses looking to safeguard their operations without breaking the bank.
If you liked this article, follow us on LinkedIn, Twitter, Facebook, and Youtube, for more cybersecurity news and topics.


