


Free EDR sounds like the easy answer to a budget problem, until you read the fine print. Several tools in popular roundups aren’t open source, some are abandoned, and most do only part of what an EDR does. This October 2026 guide covers the best open source EDR tools, what each one really does, and where a free stack needs help.
Where a commercial platform like ours is the better fit, we say so.
12 Best Open Source EDR Tools in 2026
Eleven free or open source tools are worth knowing, plus our commercial option, which we list first.
- Heimdal (commercial, not open source) for teams without the staff to run a stack, who want prevention, patching and response from one agent.
- Wazuh (4.14.9) for teams that want SIEM, endpoint monitoring and compliance reporting in one self-hosted platform, and have engineering time to tune it.
- Velociraptor (0.77.3) for incident responders and SOC analysts who need fast, fleet-wide hunting and forensic collection.
- OSSEC (4.4.1) for lightweight host intrusion detection and file integrity monitoring on servers.
- osquery (5.24.0, with Fleet) for SQL-based asset visibility and hunting telemetry that feeds a SIEM.
- GRR Rapid Response (4.0.0.0) for large organisations with in-house forensic engineers.
- OpenEDR for Windows-only estates that want a free EDR console quickly and accept a source-available licence.
- Sysmon (v15.22) for detailed Windows telemetry to feed Wazuh, Elastic, Splunk or Microsoft Sentinel.
- Fibratus (3.1.1) if your work is Windows detection engineering and research.
- Falco (0.45.1) if you run Kubernetes and need container runtime detection.
- Security Onion (3.3.0) for SOCs that want network and host visibility on one platform.
- Elastic Defend (free Basic tier) if you already run the Elastic Stack.
Versions are as of 29 October 2026.
What counts as open source EDR in 2026
EDR (endpoint detection and response) software does four jobs:
- It records endpoint activity continuously, including process, file, registry, network and user events.
- It detects suspicious behaviour in that telemetry.
- It supports investigation and root cause analysis with timelines and fleet-wide hunting.
- It takes response actions on the endpoint, such as killing a process, quarantining a file or isolating a host.
What is EDR?
 ““According to Gartner, XDR is “a comprehensive, cloud-native, and analytics-driven security offering that combines multiple security products.” Whilst that is true, my view is that to benefit and leverage XDR, you need those tools to be well integrated, which is not really what the Gartner definition says. Also, the definition is quite vague, because typically those tools are mainly reactive, whereas (and incoming advertisement alert), the Heimdal stack is heavily focused on having a proactive, predictive security posture stopping threats before they come in, which no one else really offers.””
- Morten Kjaersgaard, Founder & Chairman, Heimdal
The category grew out of Gartner analyst Anton Chuvakin’s 2013 “endpoint threat detection and response” framing. That framing centred on detection, investigation and response rather than prevention, and the open source projects still reflect it.
Very few projects do all four jobs out of the box. In our assessment, most open source EDR tools cover one or two of them well, so teams assemble a stack in three layers:
- Telemetry from Sysmon, osquery, Fibratus, Falco or the Wazuh agent.
- Detection and analytics in the Wazuh manager and indexer, Elastic or OpenSearch, Sigma rules or Security Onion.
- Investigation and response through Velociraptor, GRR, Wazuh Active Response and a case management tool.
How the category got here
- Mid-2000s. OSSEC leads host intrusion detection (HIDS), built around log analysis, file integrity monitoring (FIM) and rootkit checks.
- 2011. Google launches GRR Rapid Response, one of the first tools for hunting forensic artifacts at scale.
- 2014. Microsoft releases Sysmon in August and Facebook open-sources osquery in October.
- Around 2015. Wazuh forks OSSEC and later grows into a broader XDR and SIEM platform.
- 2018 to 2021. Mike Cohen, previously on Google’s GRR team, releases Velociraptor as a technology preview in August 2018. Rapid7 acquires the project in April 2021 and keeps it open source.
- 2019. Facebook and the Linux Foundation announce plans for an osquery foundation in June.
- 2020. Comodo releases OpenEDR, which now sits under Xcitium.
- 2021 onward. Licensing gets more complicated. Elastic changes its licence in 2021, TheHive moves to commercial licensing, and Security Onion adopts Elastic License 2.0 (ELv2) for its own code.
- 2024. Falco graduates in the Cloud Native Computing Foundation (CNCF).
Source-available is not open source
Several tools that appear in open source roundups are free to use but are not under an OSI-approved open source licence:
- OpenEDR uses the Comodo Available Source License (CASL).
- Sysmon is covered by the Microsoft Sysinternals EULA.
- Security Onion’s own code is under ELv2, and bundled tools such as Suricata and Zeek keep their own licences.
- TheHive 5 and 6 are commercial software with a free Community licence.
This matters if you plan to modify the code, host it for other parts of the business, or build a service on top of it.
What we changed in this list
Earlier versions of this article included Nessus, Snort, Ettercap, Infection Monkey, Cuckoo Sandbox, TheHive and MIG. Nessus is a proprietary vulnerability scanner. Snort, Ettercap and Infection Monkey are a network IDS, a LAN man-in-the-middle tool and an adversary emulation platform, and none of them collects endpoint telemetry or takes endpoint response actions. MIG and Cuckoo Sandbox 2.x are archived. We’ve moved the adjacent tools to their own section near the end and added Wazuh, Velociraptor, OpenEDR and the telemetry components that were missing.
Where a self-built stack falls short
Open source EDR solutions carry no licence fee. The cost moves to hardware, engineering time and the hours someone spends keeping the stack healthy. These are the gaps that show up most often once a pilot becomes production.
Agent Fatigue. A typical open source stack on a Windows host can run Sysmon for telemetry, the Wazuh agent for log shipping and FIM, osquery for state queries and a Velociraptor client for hunting. That’s four privileged agents on one machine. Each runs with high rights, has its own configuration and update cycle, and is one more piece of software an attacker can target. The human cost grows with every agent too. Each one adds a data path to check, a set of release notes to read and an alert stream to tune, and that work grows faster than headcount does.
Prevention is thin. Most open source tools detect and investigate. Few provide kernel-level blocking, exploit prevention or tamper protection. Elastic Defend’s free tier includes malware prevention, but Elastic keeps ransomware, malicious-behaviour, memory and tamper protection in its paid tiers.
Response is mostly scripted. Wazuh Active Response, for example, can block an IP address when a rule fires, and on Linux agents it can also lock a user account. That’s useful, but it’s not the same as one-click host isolation from a console.
The stack is attack surface too. A self-hosted EDR server holds sensitive data and runs with wide reach across the fleet, so it has to be patched promptly. Velociraptor 0.77.3, released in October 2026, fixes three CVEs listed in the project’s security advisories, and the same discipline applies to every server in the stack.
Scale needs planning. Wazuh 4.x documentation sets a minimum of 4 GB RAM and 2 CPU cores for indexer nodes, with 16 GB and 8 cores recommended. The all-in-one quickstart is sized for up to about 100 endpoints. Beyond that you need a distributed architecture and a retention plan.
Platform coverage is uneven. In our assessment, telemetry depth is richest on Windows, where Sysmon, Fibratus and OpenEDR run, and thinnest on macOS. None of those three has a macOS agent, and Velociraptor’s documentation states it has no quarantine capability for macOS. Test each operating system you run rather than assuming parity.
Maintenance varies by project. Mozilla archived MIG on 14 September 2019. Cuckoo Sandbox 2.x was archived in April 2021. Infection Monkey’s latest tagged release is v2.3.0 from September 2023. Check commit history and release dates before you build on any project.
Where Heimdal fits
We build Heimdal for the other side of that trade-off. An open source stack gives you source transparency and data ownership in exchange for staff time. Our platform gives you vendor-maintained prevention, detection and response in exchange for a licence fee. Neither is right for every organisation, and in practice mature teams often run a mix of both.
Every Heimdal module can be bought in three ways:
- As a standalone point product, on its own.
- As part of our unified security platform.
- As a managed service through MDR, MXDR or Managed ITDR, for teams who want the SOC run for them rather than staffed in-house.
Standalone purchase applies across the range, including NGAV with XTP, Ransomware Encryption Protection, DNS Security, Patch and Asset Management, Privileged Access Management and Email Security. Patch and Asset Management is the easiest example to picture. Say you already have a UEM or systems management tool you intend to keep, and your real gap is third-party patching, patch reporting and asset visibility. You can buy Patch and Asset Management on its own and run it alongside your existing tool rather than replacing it. From there you can stay with one module, add more, or move to the full platform.
For teams that do want the platform, the model is simple.
One agent. One console. One contract.
- Next-gen antivirus with our Extended Threat Protection (XTP) engine, plus firewall
- Ransomware Encryption Protection
- Threat-hunting and Action Center (TAC)
- DNS Security for network and endpoint
- Patch and Asset Management
- Privileged Access Management (PEDM and PASM) and Application Control with AppFencing™
- Email Security
- Unified endpoint management, including remote desktop, scripting and BitLocker management
Prevention, detection, patching and access control share one data set and one place to act.
If you want to keep Velociraptor or osquery for forensic collection, that hybrid pattern works next to a commercial platform as well. Count the extra agent when you weigh up Agent Fatigue.
Practical buyer guidance
Do you need EDR, or something next to it?
Start with the job you need done. If the requirement is “know what software is on every laptop”, osquery with Fleet may be enough. If it’s “detect and stop ransomware on endpoints”, you need prevention and response, which most open source projects do not provide on their own. If it’s “investigate an incident fast across 3,000 machines”, Velociraptor is built for that. Write the job down before you shortlist anything.
Signals an open source stack will work
- Someone on the team can own detection rules, upgrades and agent health as part of their job, not as a side task.
- You have hardware or cloud budget for indexer nodes and log retention.
- Data sovereignty or self-hosting is a hard requirement.
- You already run a SIEM such as Elastic, OpenSearch or Wazuh and want endpoint data in it.
- You value being able to read and audit every detection rule.
Warning signs
- Nobody is available to answer an alert or handle a security incident outside office hours.
- Your main requirement is blocking threats, not finding them afterwards.
- The pilot works on 50 Windows machines and you have 2,000 mixed endpoints.
- The project you like has no tagged release in more than a year.
What teams underestimate
- Tuning time. Default rules are a starting point. Poor tuning can suppress evidence along with noise.
- Storage growth. Endpoint telemetry volumes rise quickly, and retention decides your hardware bill.
- Integration work. The sensor, SIEM, case management, threat intelligence and response tools have to be connected and kept connected through upgrades.
- Patching the stack itself. Every self-hosted server needs its own update routine.
Unified, standalone or layered
A unified platform puts prevention, detection and response behind one agent and console. A standalone open source tool does one layer well and leaves you to fill the others. A layered approach, common among mature teams, pairs a commercial EDR for prevention and response with Velociraptor or osquery for hunting and forensic collection. Pick the model that matches your staffing, not the one with the longest feature list.
What this won’t fix
Open source EDR tools won’t replace an analyst. They won’t patch the vulnerable software they find, and most won’t stop an attack in progress without a script you’ve written and tested. Compliance mappings, such as Wazuh’s dashboards for PCI DSS, HIPAA, GDPR and NIST 800-53, support audit evidence. They don’t certify compliance.
How to run a proof of concept
- Start in a lab. Wazuh has an all-in-one OVA and a Docker deployment. Velociraptor runs as a single-binary server.
- Validate detections with Atomic Red Team, Red Canary’s open source library of tests mapped to MITRE ATT&CK, or a similar framework. Focus on the techniques you care about most.
- Test every response action you expect to use, on every operating system you run.
- During the pilot, measure analyst hours, false positives, agent CPU and memory overhead, and storage growth per endpoint per day.
- Project those numbers to your full estate and price a three-year total cost of ownership, including staff time.
Read the licence before you build on it
- GPL, Apache and AGPL licences are OSI-approved open source. Check their obligations if you modify the code.
- ELv2 restricts offering the software as a managed service.
- CASL limits charging for the software.
- Sysmon is freeware under a Microsoft EULA.
Best open source EDR tools compared - Top 12
Versions and status are as of October 2026. The Strong, Moderate and Limited ratings are our own assessment.
|
Tool |
Licence |
Telemetry |
Detection |
Response |
Hunting and forensics |
Platforms |
Status |
||
|---|---|---|---|---|---|---|---|---|---|
|
Heimdal (commercial) |
Commercial |
Yes |
XTP engine, 1,400+ curated rules |
One-click quarantine, isolation, block |
TAC |
Windows, macOS, Linux (module support varies) |
Active |
||
|
Wazuh |
GPLv2 (5.0 engine AGPLv3+) |
Yes (agent) |
Rules, decoders, ATT&CK mapping |
Active Response scripts |
Moderate |
Windows, Linux, macOS and others |
Active, 4.14.9 stable, 5.0 release candidate |
||
|
Velociraptor |
AGPLv3 |
On-demand plus event monitoring |
VQL monitoring, Sigma |
Quarantine (Windows, Linux), remote actions |
Strong |
Windows, Linux, macOS |
Active, 0.77.3 |
||
|
OSSEC |
GPLv2 |
Logs, FIM |
Rules |
Active Response |
Limited |
Windows, Linux, macOS, BSD, Solaris |
Active, 4.4.1 |
||
|
osquery |
Apache-2.0 or GPLv2 |
Yes (state and evented tables) |
Scheduled queries via an external manager |
None natively |
Strong (SQL) |
Windows, macOS, Linux |
Active, 5.24.0 |
||
|
GRR |
Apache-2.0 |
On-demand |
Limited |
Limited |
Strong |
Windows, macOS, Linux |
Active, 4.0.0.0 (December 2025), slower cadence |
||
|
OpenEDR |
CASL (source-available) |
Yes (kernel-level) |
Via Xcitium platform |
Via platform |
Moderate |
Windows (public repo) |
No substantive code changes since 2022 |
||
|
Sysmon |
Microsoft EULA (freeware) |
Yes |
None |
None |
Telemetry only |
Windows (Sysmon for Linux available) |
Active, v15.22 |
||
|
Fibratus |
Apache-2.0 |
Yes (Windows kernel events) |
Rule engine |
Rule actions (kill) |
Moderate |
Windows |
Active, 3.1.1 |
||
|
Falco |
Apache-2.0 |
Yes (Linux syscalls, eBPF) |
Rules |
Via Falcosidekick, Falco Talon |
Limited |
Linux, containers, Kubernetes |
Active, 0.45.1 |
||
|
Security Onion |
Mixed, including ELv2 |
Via Elastic Agent and integrations |
Sigma, Suricata and more |
Limited |
Strong (SOC platform) |
Linux server |
Active, 3.3.0 |
||
|
Elastic Defend (Basic) |
Elastic License |
Yes |
Yes, plus malware prevention |
Host isolation in paid tiers |
Moderate |
Windows, macOS, Linux |
Active |
||
Wazuh
Wazuh is a free, open source XDR and SIEM platform that forked from OSSEC around 2015. In our assessment, it’s the most complete self-hosted option on this list.
By the numbers. Version 4.14.9 (15 October 2026) and a minimum of 4 GB RAM and 2 CPU cores for indexer nodes.
Best for. Mid-market and smaller teams that want SIEM and endpoint monitoring with compliance reporting, and have engineering capacity to run it.
Strengths. The agent covers log analysis, FIM, vulnerability detection and SCA/CIS configuration checks. Rules and decoders map to MITRE ATT&CK. Active Response runs scripts that can block an IP or, on Linux agents, lock an account. Compliance mappings cover PCI DSS, HIPAA, GDPR and NIST 800-53, and Wazuh’s 5.0 release-candidate documentation adds NIS2.
Trade-offs. Expect significant tuning. Indexer resource needs grow with the number of endpoints, and the all-in-one quickstart is sized for about 100 endpoints. Prevention is limited, and response relies on scripts.
Cost and licence. The 4.x releases are under GPLv2, and Wazuh’s documentation lists Apache 2.0 for some components. In the 5.0 code on the project’s main branch, the engine is licensed under AGPLv3 or later. Self-hosting is free. As of October 2026, Wazuh lists Cloud plans from $571 a month for up to 100 agents, and paid support is available. Version 5.0 is in release candidate.
Velociraptor
Velociraptor is an open source digital forensics and incident response (DFIR) and threat-hunting platform built on its own query language, VQL. Rapid7 has owned it since April 2021 and it remains AGPL-licensed.
By the numbers. Version 0.77.3 (5 October 2026), first released as a preview in August 2018, and owned by Rapid7 since April 2021. Its documentation says one server can handle more than 10,000 endpoints.
Best for. Incident response teams and SOCs that need hunting and triage, often alongside a commercial EDR or Wazuh.
Strengths. Fleet-wide collection is fast. It has a large artifact library, offline collectors, continuous event monitoring and Sigma support, and it can quarantine Windows and Linux hosts and run remote actions. Its documentation states there is no quarantine capability for macOS.
Trade-offs. It’s not a prevention product, and it needs DFIR expertise to use well. Alerting and SIEM functions depend on forwarding data elsewhere. The server needs prompt patching, as the CVE fixes in release 0.77.3 show.
Cost and licence. Free under AGPLv3, currently on the 0.77.x release line. Support for the open source project runs through its Discord channel, mailing list and GitHub issues, and Rapid7’s product page lists Velociraptor-powered Insight agents and a partnership with its MDR service.
OSSEC
OSSEC is the original open source host-based intrusion detection system. Current release notes credit Atomicorp’s Scott Shinn as release maintainer.
By the numbers. Version 4.4.1 (18 October 2026) and six releases in 2026.
Best for. Lightweight HIDS and FIM on servers, and compliance needs such as PCI DSS file integrity monitoring.
Strengths. It is mature and light on resources. It covers log analysis, FIM, rootkit detection and Active Response, and it supports Windows, Linux, macOS, BSD and Solaris agents.
Trade-offs. It collects less endpoint telemetry than a modern EDR, and its interface is basic, so most teams pair it with an external SIEM. OSSEC’s release cadence picked up in 2026, with six releases from 4.0.0 in February to 4.4.1 on 18 October.
Cost and licence. Free under GPLv2.
osquery (with Fleet)
osquery exposes the operating system as a database you can query with SQL. It is governed under the Linux Foundation.
By the numbers. Version 5.24.0 (9 October 2026), open-sourced by Facebook in October 2014, and 292 tables in the 5.24.0 schema.
Best for. Asset visibility, compliance posture checks and hunting telemetry that feeds a SIEM.
Strengths. Visibility is flexible and cross-platform across Windows, macOS and Linux. It has YARA and FIM tables, and a broad set of companion tools, including Fleet and 1Password Device Trust (formerly Kolide).
Trade-offs. osquery isn’t EDR on its own. It has no native console, detection engine or response capability, and it needs a fleet manager to work at scale.
Cost and licence. Apache-2.0 or GPLv2. Fleet’s core is MIT-licensed and its premium features are commercially licensed.
GRR Rapid Response
GRR is Google’s remote live-forensics framework, released under Apache-2.0.
By the numbers. Version 4.0.0.0 (15 December 2025) and launched by Google in 2011.
Best for. Large organisations with in-house forensic engineering.
Strengths. It handles forensic collection at large fleet sizes across Windows, macOS and Linux.
Trade-offs. Velociraptor’s documentation describes GRR as needing a complex deployment with many moving parts, and GRR has a slower release cadence. Detection and response are limited. Version numbering differs across release artifacts, so follow the official install guide.
Cost and licence. Free under Apache-2.0.
OpenEDR (Xcitium, formerly Comodo)
Xcitium markets OpenEDR as free, open source EDR. Its licence, CASL, is source-available rather than OSI open source.
By the numbers. Latest release 2.5.1 (September 2022) and, according to Xcitium’s datasheet, three days of event storage on the hosted option.
Best for. Windows-only organisations that want a free EDR console quickly and accept the licence terms.
Strengths. It provides kernel-level Windows telemetry with ATT&CK-mapped visibility, and has both a free hosted console and a self-hosting option.
Trade-offs. The agent code in the public repository is Windows-only. Xcitium’s OpenEDR site now advertises Windows, macOS and Linux support, so check which agents the hosted platform offers before you plan for a mixed estate. According to Xcitium’s OpenEDR datasheet, the Xcitium-hosted option limits event storage to three days, uses preset security policies and carries an event data storage charge. The public repository has had no substantive code changes since September 2022, and its latest commit, in May 2026, added a security policy file. The free tier is an entry point to the commercial Xcitium platform.
Cost and licence. Free to use under CASL, which limits charging for the software.
Sysmon (telemetry component)
Sysmon is a free Microsoft Sysinternals driver that records detailed Windows activity. Since the February 2026 update KB5077241, Windows 11 versions 24H2 and 25H2 include a built-in Sysmon as an optional feature that is off by default, and Microsoft Learn also lists it for Windows Server 2025. You need to uninstall the standalone Sysinternals version before you enable it. Sysmon for Linux is available separately.
By the numbers. Standalone version v15.22 (10 September 2026), first released in August 2014.
Best for. Feeding Wazuh, Elastic, Splunk or Microsoft Sentinel.
Strengths. Telemetry quality is high, and widely used community configurations exist, including SwiftOnSecurity’s and Olaf Hartong’s sysmon-modular.
Trade-offs. It produces telemetry only, with no detection or response. It’s licensed under a Microsoft EULA, not an open source licence.
Cost and licence. Free.
Fibratus (telemetry and detection component)
Fibratus is a Windows kernel-event exploration and detection tool under Apache-2.0.
By the numbers. Version 3.1.1 (19 August 2026).
Best for. Windows detection engineering and research.
Strengths. Its rule engine ships ATT&CK-mapped rules and integrates with YARA.
Trade-offs. Release 3.1.1 is Windows-only, and the project has a small community. Initial Linux support was committed to the repository on 28 September 2026 and has not shipped in a release. Rules can trigger response actions, and Fibratus’s rule documentation shows a kill action that ends the matching process. There is no central console to run actions across a fleet.
Cost and licence. Free under Apache-2.0.
Falco (cloud-native runtime detection)
Falco is a CNCF-graduated runtime security project under Apache-2.0.
By the numbers. Version 0.45.1 (19 October 2026), CNCF graduated on 29 February 2024.
Best for. Kubernetes and container workloads.
Strengths. It detects suspicious behaviour in real time from Linux syscalls and eBPF in containers and Kubernetes. Response runs through Falcosidekick and Falco Talon.
Trade-offs. It covers Linux and cloud-native workloads only. It’s not a desktop or Windows EDR.
Cost and licence. Free under Apache-2.0.
Security Onion (SOC platform)
Security Onion is a free SOC platform covering network security monitoring, intrusion detection, log management and case management.
By the numbers. Version 3.3.0 (11 September 2026) and a standalone install minimum of 4 CPU cores, 24 GB RAM and 200 GB storage.
Best for. SOCs that want network and host visibility in one platform, and training labs.
Strengths. It has an integrated hunting interface, Suricata and Zeek for network visibility, Sigma rules, and Elastic Agent for endpoint collection.
Trade-offs. Hardware requirements are substantial. Security Onion’s own code uses ELv2, which matters if you plan to offer it as a service. It’s not a lightweight EDR. Version 2.4 reached end of life on 1 October 2026, according to Security Onion’s EOL page, so anyone still on it needs to move to 3.x.
Cost and licence. Free, with mixed licensing that includes ELv2. Paid support is available from Security Onion Solutions.
Elastic Defend (free Basic tier)
Elastic Defend is Elastic’s endpoint security integration.
Best for. Organisations already running the Elastic Stack.
Strengths. Per Elastic’s subscription table (checked 29 October 2026), the Basic tier includes endpoint telemetry and malware prevention. It builds on Elastic’s search and analytics stack.
Trade-offs. Host isolation, ransomware protection, malicious-behaviour protection, memory protection and tamper protection are in paid tiers. It isn’t OSI open source. Since 2024 Elastic has offered AGPLv3 as an option for a subset of the Elasticsearch and Kibana source code, but its binary distributions stay under the Elastic License.
Cost and licence. Basic tier is free under the Elastic License. The protections listed above need a paid subscription.
Heimdal (our commercial option)
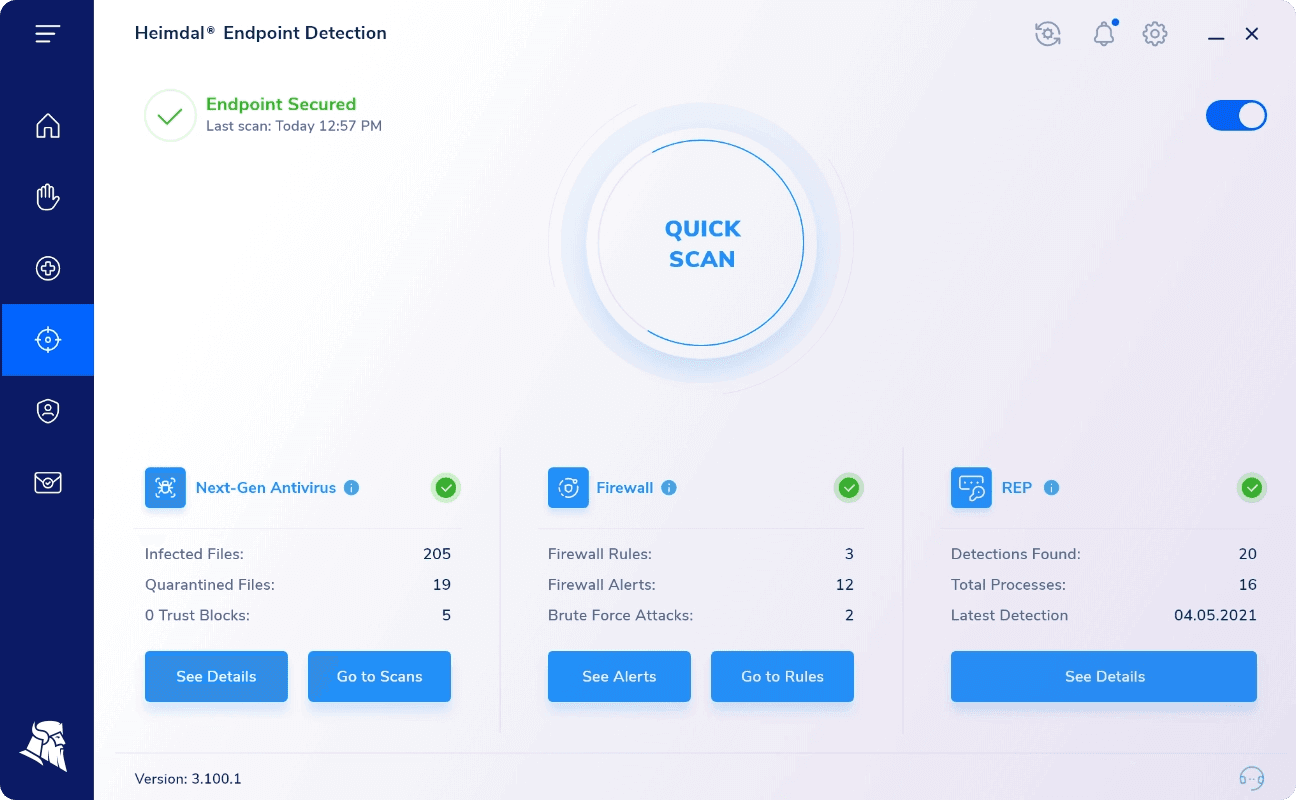
We’re not open source. We include Heimdal because the usual alternative to running an open source stack is a commercial platform, and that trade-off deserves to sit next to the free options.
What it is. A security platform where every module, including our EDR components, Patch and Asset Management, DNS Security and Privileged Access Management, can be bought on its own, combined on one agent and console, or delivered as a managed service.
Best for. Mid-market and enterprise teams that lack the staff to run and tune an open source stack, and want prevention and patching alongside detection. Confirm which modules, operating systems and response actions come with the package you’re quoted.
Strengths.
- Our NGAV runs with the XTP engine, which delivers more than 1,400 curated detection rules with MITRE ATT&CK-aligned classification. Heimdal Labs and our in-house analysts keep XTP updated with curated indicators and attack techniques, so you aren’t building that content yourself.
- The Threat-hunting and Action Center (TAC) gives one-click quarantine, isolation, scanning and blocking against the indicators it surfaces.
- Ransomware Encryption Protection X uses four detection engines (encryption, rename, shadow copy and canary) and can isolate an infected device automatically.
- Patch and Asset Management covers Microsoft, Linux, macOS and more than 350 third-party applications. Most open source stacks find vulnerable software but leave the patching to you.
- Application Control with AppFencing™, PEDM and PASM add prevention and access control that open source EDR projects do not include.
- Our DNS Security includes Predictive DNS, which uses AI and machine learning to flag malicious domains before they host malicious content. It’s a live capability today.
- The agent runs on Windows, macOS and Linux, though module support varies by operating system, so confirm it for the modules you buy.
On top of those existing capabilities we are adding AI Wingman, a cross-platform AI layer for the Heimdal platform. AI Wingman Triage uses multi-agent systems to help teams assess suspicious indicators and validate incidents, and it is included with TAC.
Trade-offs. You pay a commercial licence. As a closed-source product, our detection logic is less transparent than reading Wazuh rules or Sigma files.
Validation. We are referenced in Gartner’s Endpoint Protection coverage (May 2026). We are named as a representative vendor in Gartner’s Market Overview for Workspace Cybersecurity Platforms. We are in an active analyst relationship with Forrester. We serve over 20,000 companies.
We did not take part in MITRE ATT&CK Evaluations Enterprise 2025. Our MITRE ATT&CK technique coverage is published on the Tidal Cyber Registry, so you can review it and add it to your proof-of-concept scorecard. Map that coverage against the same techniques you test with Atomic Red Team on any open source stack.
Cost. Our pricing calculator gives an instant estimate, on the page and by email, once you enter the modules you want and your endpoint count. There is also a 30-day free trial.
Useful tools that are not EDR
These projects appeared in earlier versions of this list. They’re useful security tools, but none of them is an endpoint detection and response tool.
- Nessus is a proprietary vulnerability scanner from Tenable. As of October 2026, Nessus Essentials is free for non-commercial use only, limited to 5 IPs and issued as a 30-day licence that you re-download when it expires.
- Snort is an open source network intrusion detection and prevention system. It inspects traffic, not endpoint processes.
- Ettercap is a LAN man-in-the-middle testing tool. Use it in isolated labs.
- Infection Monkey is an open source adversary emulation platform. Its latest tagged release is v2.3.0 (September 2023), and the last commit to its development branch was on 28 February 2025.
- Cuckoo3 is CERT-EE’s malware sandbox and the successor to Cuckoo Sandbox. CERT-EE states it is not yet production-ready. Cuckoo Sandbox 2.x was archived in April 2021.
- TheHive is case management software that StrangeBee distributes commercially, with a free Community licence. Version 6.0 shipped on 20 October 2026, and TheHive 4 reached end of support on 31 December 2022.
- MIG (Mozilla InvestiGator) was archived by Mozilla on 14 September 2019 and is no longer maintained.
- LimaCharlie turns up in open source EDR roundups. It is a commercial SecOps cloud platform with a free tier and Apache-licensed SDKs, and those component licences do not make the platform open source.
Which option fits your situation
The best open source EDR tools reward teams that have time to tune rules, patch servers and read alerts. Match the choice to the team you have today.
- No SOC, a few hundred endpoints, a small IT team. Wazuh works if one person can own it. If nobody can, a commercial platform with prevention built in will cover more ground for the same headcount.
- Mid-market security team building in-house. Wazuh as the core, Sysmon on Windows hosts for richer telemetry, and Velociraptor for investigations.
- Enterprise SOC that already runs a commercial EDR. Add Velociraptor or osquery for hunting and forensic collection. Consider GRR if you have dedicated forensic engineers.
- Regulated organisation with data sovereignty rules. Self-hosted Wazuh or Security Onion keeps data on your infrastructure. Treat compliance mappings as evidence support, not certification.
- Kubernetes-heavy estate. Falco for container runtime detection, next to an endpoint tool for desktops and servers.
- Already on the Elastic Stack. Elastic Defend’s Basic tier, with budget for Enterprise or an Elastic Cloud plan if you need host isolation or tamper protection. Elastic stopped selling self-managed Platinum to new customers.
- Windows-only, need a console this week. OpenEDR, provided you accept CASL and the three-day event storage limit that Xcitium’s datasheet lists for its hosted option.
- Need prevention, patching and response without running the stack. Heimdal, as a single module, the full platform, or a managed service through MDR or MXDR.


