Network Security
 Vulnerability Management
 Privileged Access Management
 Endpoint Security
 Threat Hunting
 Unified Endpoint Management
 Email & Collaboration Security


Contents:
How to choose a WSUS replacement for endpoints, servers, and third-party apps, including options for air-gapped networks
For some teams, the trigger was a WSUS (Windows Server Update Services) sync that kept timing out through mid-July 2026 while fixes for actively exploited zero-days waited in the queue. For others, it was an out-of-band fix for a critical flaw in the WSUS server itself, or an auditor asking why browsers and PDF readers never appear in a patch report.
This guide compares ten alternatives to WSUS for enterprise and mid-market IT and security teams. It covers Microsoft’s own replacement path, cloud-native patching platforms for endpoints and Windows servers, and the tools that still work when a network has no internet connection at all.
Each profile explains what the tool does well, where it stops, and what it costs where pricing is public. The shortlist comes first.
The bottom line
If you only read one section, read this one. The best WSUS replacement for you depends on the situation you are in:
- Heimdal Patch and Asset Management. For internet-connected fleets that want Windows, macOS, Linux, and third-party patching run as a security job, bought on its own or as part of a wider security platform.
- Microsoft Intune, Windows Autopatch, and Azure Update Manager. For Microsoft 365 E3/E5 organisations with cloud-joined clients that want to use licences they already pay for.
- Microsoft Configuration Manager. For large enterprises already invested in ConfigMgr, needing granular on-premises control and able to live with its WSUS dependency.
- ManageEngine Patch Manager Plus. For cost-sensitive teams that need multi-OS patching with a genuine choice between cloud and on-premises, including segmented networks.
- Automox. For distributed, remote-first organisations after cloud-native, cross-OS patching with scripting.
- Ivanti Neurons for Patch Management. For large mixed-OS enterprises that need risk-based prioritisation and SLA tracking, and have experienced admins to run it.
- NinjaOne. For IT teams that want patching, monitoring, and remote access in one easy-to-learn cloud console.
- Action1. For mostly Windows fleets that want cloud patching free for the first 200 endpoints.
- PDQ Deploy & Inventory and PDQ Connect. For Windows-centric sysadmin teams after simple, package-driven deployment, on-premises or in the cloud.
- BatchPatch. For small Windows shops and air-gapped Windows networks that need lightweight orchestration, including offline scanning.
WSUS alternatives at a glance
| Vendor | Best For | OS Coverage | Third-Party Apps | Pricing |
|---|---|---|---|---|
| Heimdal | Mid-market and enterprise organisations with internet-connected fleets that want OS and third-party patching in one place, tied into their wider security stack when they are ready. | Windows, macOS, Linux (Debian, Ubuntu) | 350+ apps and drivers | Instant estimate via our pricing calculator |
| Microsoft (Intune/Autopatch) | Microsoft 365 E3/E5 or Business Premium organisations with Entra-joined or hybrid-joined clients. | Windows | Microsoft catalogue via Enterprise App Management | Autopatch included with qualifying licences. Add-ons priced separately |
| Microsoft (Configuration Manager) | Large enterprises with an existing ConfigMgr investment, especially those moving gradually to Intune through co-management. | Windows | Limited without add-ons | Microsoft licensing |
| ManageEngine | Cost-sensitive mid-market organisations, including those with segmented or DMZ networks. | Windows, macOS, Linux | 1,100+ | From $245 per year for 50 computers (on-prem Professional) |
| Automox | Distributed organisations that want cross-OS patching over the internet with room for custom automation. | Windows, macOS, Linux | 630+ | About $2.57 to $2.93 per endpoint per month at 1,500 endpoints |
| Ivanti | Large enterprises with mixed-OS environments and formal patch SLAs. | Windows, macOS, Linux | 800+ | Quote-based |
| NinjaOne | Mid-market IT teams that want patching and day-to-day endpoint management in one cloud console. | Windows, macOS, Linux | “Thousands” | Published range of about $1.50 to $3.75 per device per month, depending on volume. Final pricing by quote |
| Action1 | Small and mid-market fleets that are mostly Windows, particularly those under 200 endpoints. | Windows, Linux (Debian, Ubuntu) | Vendor catalogue | Free up to 200 endpoints. Paid from about $4 per endpoint per month |
| PDQ | Windows-centric sysadmin teams that want simple, package-driven software deployment and patching. | Windows / Windows and macOS | Prebuilt package library | $1,950 per admin per year / $12 to $28 per device per year |
| BatchPatch | Small Windows shops, and air-gapped Windows networks that need a WSUS server alternative with minimal infrastructure. | Windows | Limited | Per-user licence. Prices not listed in text on the purchase page |
How patch management moved on from WSUS
WSUS launched in 2005, years before cloud computing reshaped IT, for a world where devices sat on the corporate LAN, most software came from Microsoft, and patching ran on a monthly rhythm. From then until the shift to remote work around 2020, patching was centralised, on-premises, and Windows-focused. WSUS and SCCM defined the category.
Remote work, SaaS, and mixed-OS fleets changed that. Laptops stopped coming back to the office network. Browsers, Java, Adobe products, and Zoom became as important to patch as Windows itself. Buyers moved toward cloud-native, agent-based tools that patch over the internet.
Between 2024 and 2026, three things pulled patching closer to vulnerability and exposure management:
- Microsoft deprecated WSUS
- WSUS itself became a high-profile attack target
- Vulnerability exploitation kept rising
The last point shows up clearly in breach data. In the 2026 Verizon DBIR, exploitation of vulnerabilities became the most common initial access vector for the first time, at 31% of breaches. In the 2025 edition it was 20%.
Market sizing is less precise. Mordor Intelligence puts the global patch management market at $3.01B in 2026, growing to $4.54B by 2031. Other firms publish figures under $1B because they define the category more narrowly, so treat any single number as directional.
What WSUS deprecation actually means
Microsoft announced WSUS deprecation on 20 September 2024. WSUS deprecation means Microsoft will no longer develop new features for it, and it will not take new feature requests. It’s still an included, supported role in Windows Server 2025, and Microsoft says it has no current plans to remove it from in-market Windows Server versions.
Windows Server 2025 extended support ends on 14 November 2034. Microsoft has published no WSUS-specific end date. Because WSUS ships in Server 2025, it could plausibly stay usable into the mid-2030s. That’s an inference from the lifecycle, not a Microsoft commitment.
Four assumptions that trip up WSUS replacement projects
“WSUS is being shut down.” It’s deprecated, not removed. Deprecation creates a reason to plan a migration, not a deadline to finish one.
“WSUS is free.” There’s no licence fee. There’s a server, a SQL or WID database, storage, IIS, and regular SUSDB maintenance. Microsoft maintains a dedicated WSUS maintenance guide because the database and application pool need ongoing care.
“Intune replaces WSUS one-for-one.” Intune uses cloud policy controls. It doesn’t give you a locally hosted update catalogue and approval console. Teams used to approving individual updates need to rethink their process, not just their tooling.
“Autopatch patches everything.” Windows Autopatch covers Microsoft client content only. Windows Server and most third-party applications sit outside it.
Where WSUS and traditional patching fall short
These are the gaps that most often turn a WSUS replacement from a someday project into a current one.
The WSUS server is now an attack surface. CVE-2025-59287 is a critical (CVSS 9.8) unauthenticated remote code execution flaw in the WSUS reporting web service. Microsoft’s regular October 2025 update did not fully fix it, so out-of-band updates followed on 23 October 2025. Huntress and Palo Alto Networks Unit 42 reported exploitation within hours, aimed at WSUS instances exposed on ports 8530 and 8531. CISA added it to the Known Exploited Vulnerabilities catalogue the next day. A patching server with no new feature development is still a server you have to patch and harden.
Sync reliability is not guaranteed. In July 2026, Microsoft confirmed WSUS synchronisation slowdowns and timeouts that worsened from around 13 July. A service-side mitigation arrived on 18 July, but existing servers still needed a manual SUSDB cleanup documented in KB5121986. Press coverage reported that some organisations delayed July security updates as a result, including fixes for actively exploited zero-days.
Third-party applications are invisible. WSUS only covers Microsoft products. Browsers, PDF readers, Java, Zoom, and the rest of a typical software estate need a separate process, which in many organisations is still manual.
Remote devices drift. WSUS assumes a device can reach the server. Laptops working from home without a VPN (virtual private network) connection fall out of patch compliance quietly, and nobody sees it until an audit or an incident.
No risk-based prioritisation. WSUS treats updates by Microsoft classification. It has no native way to put a CISA KEV-listed vulnerability ahead of a routine fix using CVSS or EPSS data.
Compliance evidence takes manual work. Frameworks such as NIS2, DORA, PCI DSS, HIPAA, Cyber Essentials, and Essential Eight expect evidence of patch SLAs over time. A WSUS report showing what’s installed today doesn’t answer “how long did that critical patch take to reach every device?”
Agent fatigue. Replacing WSUS with a stack of point tools creates its own problem. One agent for OS patching, another for third-party apps, a vulnerability scanner, an endpoint protection agent, and a remote access tool means several privileged agents on every host. Published detection guidance increasingly flags that kind of agent footprint as a security risk indicator in its own right. The human cost grows too. Every extra agent is another console to check, another update cycle to track, and another alert stream to triage, and that load compounds faster than headcount does.
Why we treat patching as a security job
At Heimdal, we built Patch and Asset Management on a simple premise. An unpatched vulnerability is an open door, and the time between disclosure and exploitation keeps shrinking. Patching belongs next to the rest of your security controls, not in a separate IT maintenance queue.
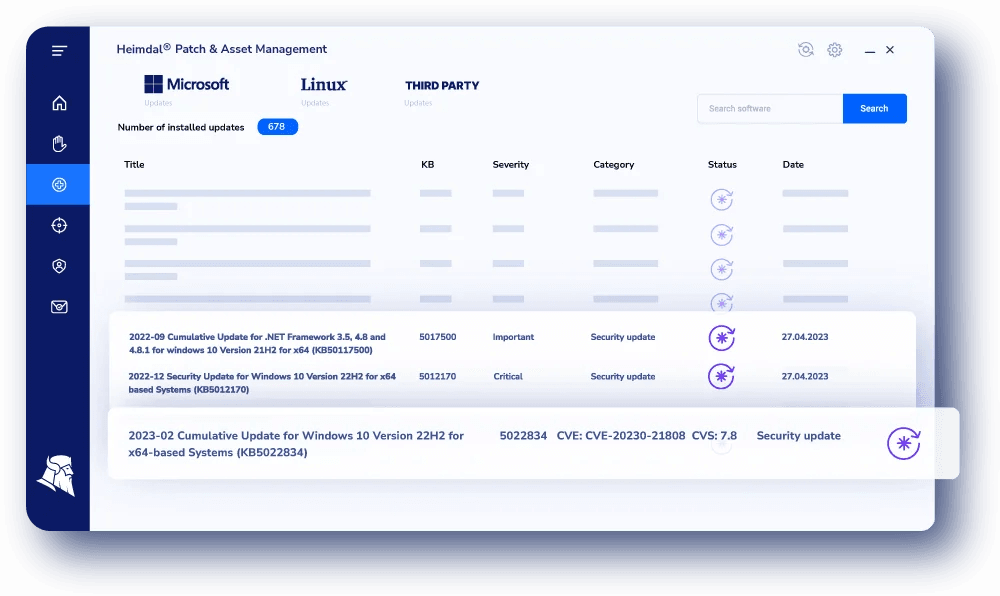
!Screenshot from Heimdal’s Patch and Asset Management software
We sell our platform three ways, and every module works with all three.
1. As a standalone point product. Every Heimdal module can be bought on its own, from Patch and Asset Management to email security. You scale up or down into exactly what you need, up to the full platform if you want it.
Patch and Asset Management is an easy example. Say you already run Intune or another endpoint management tool and plan to keep it. Your real gap is third-party patching, patch reporting, and asset visibility. You can buy our Patch and Asset Management on its own, and it runs alongside your existing tool rather than replacing it.
2. As part of our unified security platform. One agent. One console. One contract. The platform brings together:
- DNS security at network and endpoint level, including Predictive DNS
- Next-generation antivirus, firewall, and ransomware encryption protection
- Privileged access management (PEDM and PASM) and Application Control with AppFencing™
- Email security with AI-powered fraud prevention
- The Threat-hunting and Action Center for estate and M365 user monitoring
- Patch and Asset Management, plus endpoint management tools such as remote desktop, scripting, and BitLocker management
When patching runs inside the platform, you manage it next to the vulnerability and threat context from the rest of your estate, not in a silo.
3. As a managed service. If you would rather have the SOC run for you than staff it in-house, we deliver MDR, MXDR, and Managed ITDR with 24/7 analysts on the same platform.
Some of our platform already uses AI and machine learning in production. Predictive DNS uses AI/ML-driven analysis to identify malicious domains before threats fully materialise. Our email security uses AI-powered outlier detection to catch impersonation, CEO fraud, and anomalous behaviour. Both are live capabilities that predate our newer AI programme.
That newer programme is AI Wingman, a separate cross-platform intelligence layer we are building on top of these capabilities and delivering in phases:
- AI Wingman Assist gives platform guidance so teams get value faster
- AI Wingman Triage uses multi-agent systems (MAS) to validate incidents, and is included with the Threat-hunting and Action Center
- AI Wingman SOC accelerates our managed SOC for customers using TAC and MXDR
For patching specifically, AI/ML-driven patch sequencing is one of the native AI capabilities we are building. It’s designed to get the most remediation value out of limited maintenance windows.
We’re not the right answer for every WSUS replacement. We’re cloud-only, so air-gapped networks need a different tool. If you run a small, Windows-only fleet, a lighter tool may cover you for less. We say where those lines sit in our profile below.
How to evaluate a WSUS replacement
Do you need to replace WSUS right now?
Not always. WSUS may still be enough if all of these are true:
- Your fleet is Windows-only and on the corporate network
- You have fewer than about 200 devices
- You apply security updates promptly and keep the WSUS server off the internet
- Your auditors are satisfied with your current evidence
If that’s you, patch the WSUS server, plan a migration, and revisit it at your next hardware or licensing cycle.
Signals that it is time to move
- Macs or Linux servers sit outside your patching process
- Third-party apps are patched by hand, or not at all
- Remote laptops show up in reports weeks after a patch release
- You spend hours each month on SUSDB cleanup, sync failures, or IIS pool crashes
- Auditors ask for patch SLA evidence and producing it takes days
- The July 2026 sync problem delayed your security updates
First, map what your Microsoft licences already cover
Many organisations already pay for part of a WSUS replacement. Check these before you buy anything:
- Windows Autopatch is included with Windows 10 and Windows 11 Enterprise E3/E5, Microsoft 365 E3/E5/F3, Microsoft 365 Business Premium, and Education A3/A5. Some capabilities vary by tier. It needs Intune and Microsoft Entra join or hybrid join.
- Intune Enterprise App Management costs $2 per user per month standalone or comes in the Intune Suite at $10 per user per month. Microsoft announced it would be included in Microsoft 365 E5 from July 2026, so confirm your specific entitlement.
- Azure Update Manager, part of Microsoft Azure, has no separate charge for Azure VMs. Azure Arc-enabled on-premises servers cost up to $5 per server per month, unless an entitlement such as Defender for Servers Plan 2 waives it.
The gaps that remain are usually Windows Server outside Azure, third-party apps beyond Microsoft’s catalogue, and non-Windows devices. That remainder is what you are really shopping for.
What mid-market teams underestimate
Catalogue coverage for your apps matters more than catalogue size. Vendor-stated catalogues in this guide range from a few hundred titles to over a thousand. A bigger number only helps if it includes the software you run. Export your installed software list and check it against each shortlisted vendor.
Deployment model has to match reality. Cloud-native tools suit remote-first fleets. They do not suit air-gapped or classified networks. If you have both, you may run two tools, or keep WSUS for the disconnected segment.
Compliance reporting is not the same as a dashboard. Ask each vendor for a sample audit export mapped to your framework, with historical patch timing, not a screenshot of a status page.
Migration cleanup takes real time. Leftover WSUS Group Policy and registry settings often conflict with a new tool. Plan to remove them as a standard migration step.
How to run a proof of concept
Shortlist two to four tools. A mid-market PoC usually takes a few weeks, and an enterprise PoC can take a few months. During the pilot:
- Deploy to a representative group, including remote laptops, each OS you run, and at least one server
- Test patching for your own third-party apps, not the vendor’s demo list
- Run a full cycle end to end, from release to confirmed install, and time it
- Test a rollback on a non-critical system
- Check how patch integrity is protected, what privileges the agent runs with, and which SOC 2 or ISO certifications the vendor holds
- Review each vendor’s own security advisory history as part of your vendor-risk assessment
- Track admin hours per week once setup is done
Keep WSUS running for the rest of the fleet during the pilot. A phased migration from WSUS reduces the risk of coverage gaps.
What patch management will not fix
Patching fixes known vulnerabilities in supported software. It does nothing for zero-days before a fix exists, misconfigurations, end-of-life software, or credential and phishing risk. If patching is your main security control, those gaps need separate attention.
WSUS and its alternatives compared
WSUS (the incumbent baseline)
WSUS syncs Microsoft update metadata and binaries into a local store, lets you approve updates for computer groups, distributes them over the LAN, and gives basic compliance reports.
Where it still fits. Air-gapped and disconnected networks, where Microsoft’s cloud services cannot reach. Small Windows-only estates with stable needs.
Strengths
- No licence fee
- Supported in Windows Server 2025, with no announced removal date
- Works without internet connectivity at the client end
- Driver sync still works. Microsoft planned to end it on 18 April 2025, then postponed the change in early April 2025 after customer feedback, particularly from disconnected networks. No new date has been published.
Trade-offs
- No new features, and no third-party, macOS, or Linux patching
- No reach to remote devices without VPN
- The server needs hardening. Apply the October 2025 out-of-band updates for CVE-2025-59287 (for example KB5070881 on Server 2025 and KB5070884 on Server 2022) and never expose ports 8530 or 8531 to the internet.
- Ongoing SUSDB maintenance, plus fixes like the KB5121986 cleanup after the July 2026 sync issue
Pricing. No licence fee. Budget for server, database, storage, and admin time.
Heimdal Patch and Asset Management
We built Heimdal Patch and Asset Management for teams that want patching to work as a security function. You can buy it on its own, just like any of our modules, or run it inside our unified platform. It can also run alongside your existing WSUS infrastructure while you migrate.
Best for. Mid-market and enterprise organisations with internet-connected fleets that want OS and third-party patching in one place, tied into their wider security stack when they are ready.
Key strengths
- Patch management across Windows (8 and up, Server 2012 and up), macOS, and Linux (Debian and Ubuntu) from one console
- Monitoring and patching for 350+ third-party applications and drivers, per our current catalogue
- Our target is to deliver patches in under 4 hours from vendor release, after we test and repackage them in our sandbox. Packages are encrypted in transit.
- Local P2P distribution and Priority Server Updates for bandwidth-limited sites
- Configurable scheduling, ring-style prioritisation, and rollback
- Compliance reporting that we map to GDPR, NIS2, Cyber Essentials, CIS Controls, NIST, ISO 27001, DORA, and Essential Eight, with a CVE and CVSS audit trail
- Software inventory showing assets, versions, and volumes
- Infinity Management add-on for patching custom and in-house software on Windows and Linux
- 24/7 support
Trade-offs
- Cloud-only. We don’t support on-premises or hybrid deployments, so we’re not a fit for air-gapped networks. For those, look at WSUS itself, BatchPatch, Configuration Manager, or ManageEngine’s on-premises edition.
- Our 350+ title catalogue is smaller than several competitors’ stated catalogues. Check it against your software list during a PoC.
- Some G2 reviewers report weaker high-level reporting and dashboards, and limited reboot control.
- For a small Windows-only fleet, the platform may be more than you need.
Where we sit on RMM. We didn’t start as an RMM vendor. Our starting point was security. Even so, a meaningful number of customers already run Heimdal as their day-to-day endpoint management tool, and we keep adding capability, such as remote desktop, scripting, and PXE deployment, that makes that move easier.
Independent validation. In May 2026, Gartner named us in the Europe Context Magic Quadrant for Endpoint Protection, a regional supplementary report rather than the global Magic Quadrant. In August 2026, we were listed as a representative vendor in Gartner’s Market Overview for Workspace Cybersecurity Platforms, alongside vendors including Microsoft, CrowdStrike, and Sophos. We are also in an analyst relationship with Forrester and expect a report to be published soon.
Our MITRE ATT&CK coverage is publicly mapped on the Tidal Cyber Registry. Search for Heimdal and you can see exactly which attack techniques and sub-techniques we detect and stop, down to the sub-technique level. We haven’t paid to participate in the MITRE Engenuity Evaluations, which are a vendor-funded programme. Our coverage is transparent and independently verifiable at any time. If you are consolidating patching with endpoint security, pull the mapping into your PoC scorecard and compare it directly against any other vendor you are evaluating.
Pricing. Priced per device per year. Pick your modules and endpoint count in our pricing calculator for an instant estimate on the page and by email.
Microsoft Intune, Windows Autopatch, and Azure Update Manager
This is Microsoft’s own WSUS successor path. It’s not one product. It combines Intune with Windows Update client policies (formerly Windows Update for Business) and Autopatch for clients, Azure Update Manager for servers, and Connected Cache with Delivery Optimization for bandwidth.
Best for. Microsoft 365 E3/E5 or Business Premium organisations with Entra-joined or hybrid-joined clients.
Key strengths
- Many organisations already hold qualifying licences for Autopatch
- Autopatch automates ring-based servicing for Windows quality and feature updates, Microsoft 365 Apps, Edge, and Teams
- Deep Windows integration and no on-premises update server to maintain
- Hotpatch for Windows Server 2025 via Azure Arc applies security updates without a reboot, now at no additional charge
- Enterprise App Management adds third-party apps from Microsoft’s catalogue
Trade-offs
- Several separate services to configure and license
- Autopatch does not cover Windows Server or general third-party applications
- Enterprise App Management costs extra outside Microsoft 365 E5, and its catalogue is narrower than dedicated tools
- Arc charges apply to on-premises servers
- Internet access is required, so it does not serve air-gapped networks
- No macOS or Linux patching in the WSUS sense
Pricing. Autopatch is included with qualifying licences. Azure Update Manager has no separate charge for Azure VMs and costs up to $5 per Arc-enabled server per month. Hotpatch for Windows Server 2025 via Azure Arc is no longer billed separately. Microsoft discontinued the earlier $1.50 per CPU core per month subscription in 2026 and now includes it at no additional Arc charge. Enterprise App Management is $2 per user per month standalone or part of the $10 Intune Suite.
Microsoft Configuration Manager
Configuration Manager (MECM, formerly SCCM) is Microsoft’s on-premises enterprise management platform. It’s not deprecated. Its on-premises software update point relies on the WSUS role, so ConfigMgr-based patching keeps an indirect WSUS dependency.
Best for. Large enterprises with an existing ConfigMgr investment, especially those moving gradually to Intune through co-management.
Key strengths
- Mature, granular control over deployment, targeting, and maintenance windows
- Works on-premises and in disconnected networks
- Co-management with Intune is Microsoft’s standard transition pattern
Trade-offs
- Complex to run and staff
- Software updates depend on WSUS, so you inherit its maintenance and hardening needs
- Third-party patching is limited without add-ons such as Patch My PC
Pricing. Licensed through Microsoft agreements. Most organisations considering it already own it.
ManageEngine Patch Manager Plus
ManageEngine Patch Manager Plus is a dedicated, cross-platform patching tool available as cloud or on-premises. That choice is rare in this list. Unlike WSUS, it covers macOS and Linux as well as Windows.
Best for. Cost-sensitive mid-market organisations, including those with segmented or DMZ networks.
Key strengths
- Windows, macOS, and Linux support
- ManageEngine states coverage for 1,100+ third-party applications (older datasheets cite 850+)
- Distribution servers and a secure gateway for DMZ and segmented networks
- Automated test-and-approve workflows in the Enterprise edition
- Free edition for small environments
Trade-offs
- Some reviewers describe the interface as dated
- Advanced features, including test-and-approve, require the Enterprise edition
Pricing. For 50 computers and one technician (ManageEngine price page, September 2026):
- Professional costs $245 per year on-premises or $345 per year in the cloud
- Enterprise costs $345 per year on-premises or $445 per year in the cloud
Automox
Automox is a cloud-native patching platform built for remote-first fleets. There is no on-premises infrastructure to run.
Best for. Distributed organisations that want cross-OS patching over the internet with room for custom automation.
Key strengths
- Windows, macOS, and Linux from one console
- Automox states support for 630+ third-party titles (live pricing calculator, September 2026)
- Worklets let admins script custom remediation for edge cases
- Integrations with vulnerability scanners for risk-informed patching
Trade-offs
- No on-premises or air-gapped option
- Getting full value from Worklets requires scripting skills
Pricing. Automox’s public pricing calculator shows about $2.57 to $2.93 per endpoint per month at 1,500 endpoints, depending on tier, with annual commitment (September 2026).
Ivanti Neurons for Patch Management
Ivanti Neurons for Patch Management is an enterprise platform built around risk-based prioritisation.
Best for. Large enterprises with mixed-OS environments and formal patch SLAs.
Key strengths
- Ivanti’s proprietary Vulnerability Risk Rating (VRR) for prioritisation beyond CVSS
- Ivanti states coverage for 800+ third-party titles
- Cross-OS coverage
- SLA tracking for compliance reporting
Trade-offs
- Complex, and needs experienced administrators
- Most value comes inside the wider Ivanti platform
Pricing. Quote-based. Contact Ivanti.
NinjaOne
NinjaOne is a unified RMM and endpoint management platform. Patching is one core module alongside monitoring, remote access and alerting.
Best for. Mid-market IT teams that want patching and day-to-day endpoint management in one cloud console.
Key strengths
- Usability is consistently rated highly on review sites
- NinjaOne documents Linux patch policies alongside Windows and macOS patching
- NinjaOne states it can patch thousands of third-party applications. Confirm coverage for your own software during evaluation.
- Patching, monitoring, and remote access in one agent
Trade-offs
- Cloud-only, with no option for air-gapped networks
- Patching is one module in a broader IT operations product, so check reporting depth against your audit needs
Pricing. NinjaOne’s published range is about $1.50 to $3.75 per device per month, falling with volume (to about $1.50 at 10,000+ endpoints). Final pricing is quote-based, so verify with NinjaOne.
Action1
Action1 is a cloud-native patching platform with a generous free tier.
Best for. Small and mid-market fleets that are mostly Windows, particularly those under 200 endpoints.
Key strengths
- Free for the first 200 endpoints, with no feature limits
- OS and third-party patching from the cloud
- Linux support for Debian and Ubuntu
- SOC 2 Type II and ISO/IEC 27001 certified
Trade-offs
- Cloud-only
- Narrower Linux distro coverage than some competitors
- A smaller vendor than most in this list
Pricing. Free up to 200 endpoints. Paid tier advertised from about $4 per endpoint per month (September 2026).
PDQ Deploy & Inventory and PDQ Connect
PDQ builds Windows deployment tools for sysadmins. Deploy & Inventory is the on-premises product. Connect is the cloud product. They are licensed very differently.
Best for. Windows-centric sysadmin teams that want simple, package-driven software deployment and patching.
Key strengths
- Prebuilt package library for common applications
- Simple to learn and use
- Deploy & Inventory works on the LAN with no cloud dependency
- Connect patches off-network devices and adds macOS
Trade-offs
- Deploy & Inventory is Windows-only and LAN-based, so it does not suit remote fleets
- Connect lists no Linux support
- Automated deployments in Connect require the Plus tier, and vulnerability scanning and prioritisation require Premium
Pricing. From pdq.com, 25 September 2026:
- Deploy & Inventory costs $1,950 per admin per year, with unlimited endpoints
- Connect costs $12, $18, or $28 per device per year for Basic, Plus, and Premium, with a 100-device minimum
BatchPatch
BatchPatch is a lightweight Windows patch management and orchestration tool. It can pull updates from Windows Update, Microsoft Update or an existing WSUS server.
Best for. Small Windows shops, and air-gapped Windows networks that need a WSUS server alternative with minimal infrastructure.
Key strengths
- According to BatchPatch’s documentation, Cached Mode and Offline Mode use Microsoft’s wsusscn2.cab scan file, so disconnected machines can still be scanned and patched
- In practice, Offline Mode is the closest widely used alternative to WSUS Offline Update
- Remote command execution across many machines
- Minimal setup and no server infrastructure of its own
Trade-offs
- Windows-only
- Limited third-party coverage
- No cloud console
- Manual effort grows quickly on large fleets
Pricing. Licensed per user. At the time of writing, prices are not listed in text on the public purchase page.
Others worth knowing about
- Kaseya VSA and N-able N-sight/N-central. RMM platforms built mainly for MSPs, with patching included.
- SolarWinds Patch Manager. Extends WSUS and ConfigMgr with third-party patching, so it keeps the WSUS dependency.
- Tanium. Real-time endpoint management for very large enterprises.
- Patch My PC. A third-party catalogue that plugs into ConfigMgr and Intune. It pairs well with Microsoft’s stack if third-party apps are your only gap.
Choosing the right WSUS replacement for your situation
If you have air-gapped or disconnected networks, cloud-only tools are off the table for those segments. Keep WSUS there, or look at BatchPatch’s Offline Mode, ConfigMgr, or ManageEngine Patch Manager Plus on-premises. Many organisations run one tool for connected devices and another for the disconnected segment.
Already paying for Microsoft 365 E3/E5? Start with Autopatch and Intune for clients, then decide how to cover Windows Server, third-party apps, and any Macs or Linux machines. That remainder may be Azure Update Manager plus Enterprise App Management, or a dedicated tool running alongside Intune.
If you are a large ConfigMgr shop, co-management with Intune is the lowest-disruption route. Budget for a third-party catalogue and remember the WSUS role stays underneath.
Consolidating your security stack? Heimdal Patch and Asset Management gives you OS and third-party patching on its own today, with the option to add DNS security, endpoint protection, PAM, and email security on the same agent later. It’s the right fit when you want fewer agents and consoles, and your fleet is internet-connected.
If your fleet is remote-first and you like to script, Automox gives you cross-OS cloud patching with Worklets for custom fixes.
Want patching and endpoint management in one easy console? NinjaOne is quick to adopt. Check its patch reporting against your audit requirements.
If you run a large, mixed-OS estate with formal SLAs, Ivanti Neurons offers mature risk scoring. Plan for the admin expertise it needs.
Working with the tightest budget? Action1 is free up to 200 endpoints and ManageEngine starts at a few hundred dollars a year for 50 computers. For Windows-only LAN environments, PDQ Deploy & Inventory’s per-admin pricing can work out cheaply at scale.
Do not choose on feature count. Choose on OS coverage, catalogue fit for your software, deployment model, reporting evidence, and the admin time your team will actually spend.
Frequently asked questions
Is WSUS being discontinued or reaching end of life?
No. Microsoft deprecated WSUS in September 2024, which means no new features. It remains a supported role in Windows Server 2025 and Microsoft has no current plans to remove it from in-market versions. Server 2025 extended support runs to November 2034, so WSUS could plausibly stay usable into the mid-2030s, although Microsoft has not committed to a WSUS-specific date.
Is WSUS or SCCM (Configuration Manager) better for Windows updates?
They are not really alternatives to each other. SCCM, now Configuration Manager, uses WSUS as its software update point, so it inherits WSUS’s maintenance and hardening needs rather than replacing them. Configuration Manager adds far more granular targeting, reporting, and application deployment on top, but it does not remove the WSUS dependency underneath. Large enterprises already running Configuration Manager typically keep it and co-manage with Intune. Teams without that investment are usually better served by a purpose-built WSUS replacement rather than adopting Configuration Manager just for patching.
Is WSUS still safe to use in 2026?
It can be, if you maintain it. Apply the October 2025 out-of-band updates for CVE-2025-59287, keep ports 8530 and 8531 off the internet, and run regular SUSDB maintenance. If you were affected by the July 2026 sync problems, follow the cleanup steps in KB5121986.
What is Microsoft’s official WSUS successor?
There’s no single successor. Microsoft points clients to Intune with Windows Update client policies and Windows Autopatch, servers to Azure Update Manager, and bandwidth to Connected Cache and Delivery Optimization. That spreads update management across several services rather than one console. Third-party apps can be added through Intune Enterprise App Management. All of these need internet connectivity.
Does Windows Autopatch replace WSUS?
Only for part of the job. Autopatch covers Windows quality and feature updates, Microsoft 365 Apps, Edge, and Teams on Intune-managed, Entra-joined or hybrid-joined clients. It does not cover Windows Server or general third-party applications.
Did WSUS driver sync end in April 2025?
No. Microsoft announced it would end on 18 April 2025, then postponed the change in early April 2025 after customer feedback. As of September 2026, driver sync still works and no new end date has been published.
What is the best WSUS alternative for air-gapped networks?
Cloud-native tools will not work there. Common choices are WSUS itself, BatchPatch with Offline Mode, Configuration Manager, or ManageEngine Patch Manager Plus on-premises.
What happened to WSUS Offline Update?
WSUS Offline Update is an unrelated community tool, not a Microsoft product. Both the original project and a separately maintained community edition (wsusoffline CE) are available, and the original project’s GitLab repository shows releases as recent as September 2026. For teams that want an alternative, BatchPatch’s Offline Mode, which uses Microsoft’s wsusscn2.cab scan file, is the closest widely used option.
What is a good BatchPatch alternative?
It depends on why you are moving. If your fleet has outgrown manual orchestration but stays on-premises, PDQ Deploy & Inventory or ManageEngine Patch Manager Plus on-premises add automation and reporting. If your devices are internet-connected and you need third-party, macOS, or Linux coverage, a cloud platform such as Heimdal, Automox, NinjaOne, or Action1 is the bigger step up.
Can I run a new tool alongside WSUS during migration?
Yes. Most organisations run WSUS in parallel with a new tool, migrating a pilot group first while WSUS covers the rest. Remove leftover WSUS Group Policy and registry settings from migrated devices, because they often conflict with the new tool.
How much does a WSUS replacement cost?
Published prices as of September 2026 include:
- Action1. Free up to 200 endpoints, then from about $4 per endpoint per month
- ManageEngine Patch Manager Plus. From $245 per year for 50 computers on-premises
- PDQ. Connect costs $12 to $28 per device per year, and Deploy & Inventory costs $1,950 per admin per year
- Automox. About $2.57 to $2.93 per endpoint per month at 1,500 endpoints
- Microsoft. Autopatch is included with qualifying licences, Arc-enabled servers cost up to $5 per server per month, and Hotpatch via Azure Arc now comes at no additional charge (the former $1.50 per core per month fee was discontinued in 2026)
Heimdal gives an instant estimate through our pricing calculator. Ivanti is quote-based. NinjaOne publishes a range of about $1.50 to $3.75 per device per month, with final pricing by quote. Add admin time to every comparison, because it is often the larger cost.
What is risk-based patch prioritisation and do I need it?
It means ordering patches by how likely and how damaging exploitation would be, using CVSS scores, EPSS probabilities, and the CISA KEV catalogue, rather than by release date. With vulnerability exploitation now the leading initial access vector in the 2026 Verizon DBIR, it is worth having for any organisation with more than a few hundred endpoints or compliance obligations.